
LoRaWAN Gateway Network Segmentation Guide: VLAN, Firewall and LNS Access
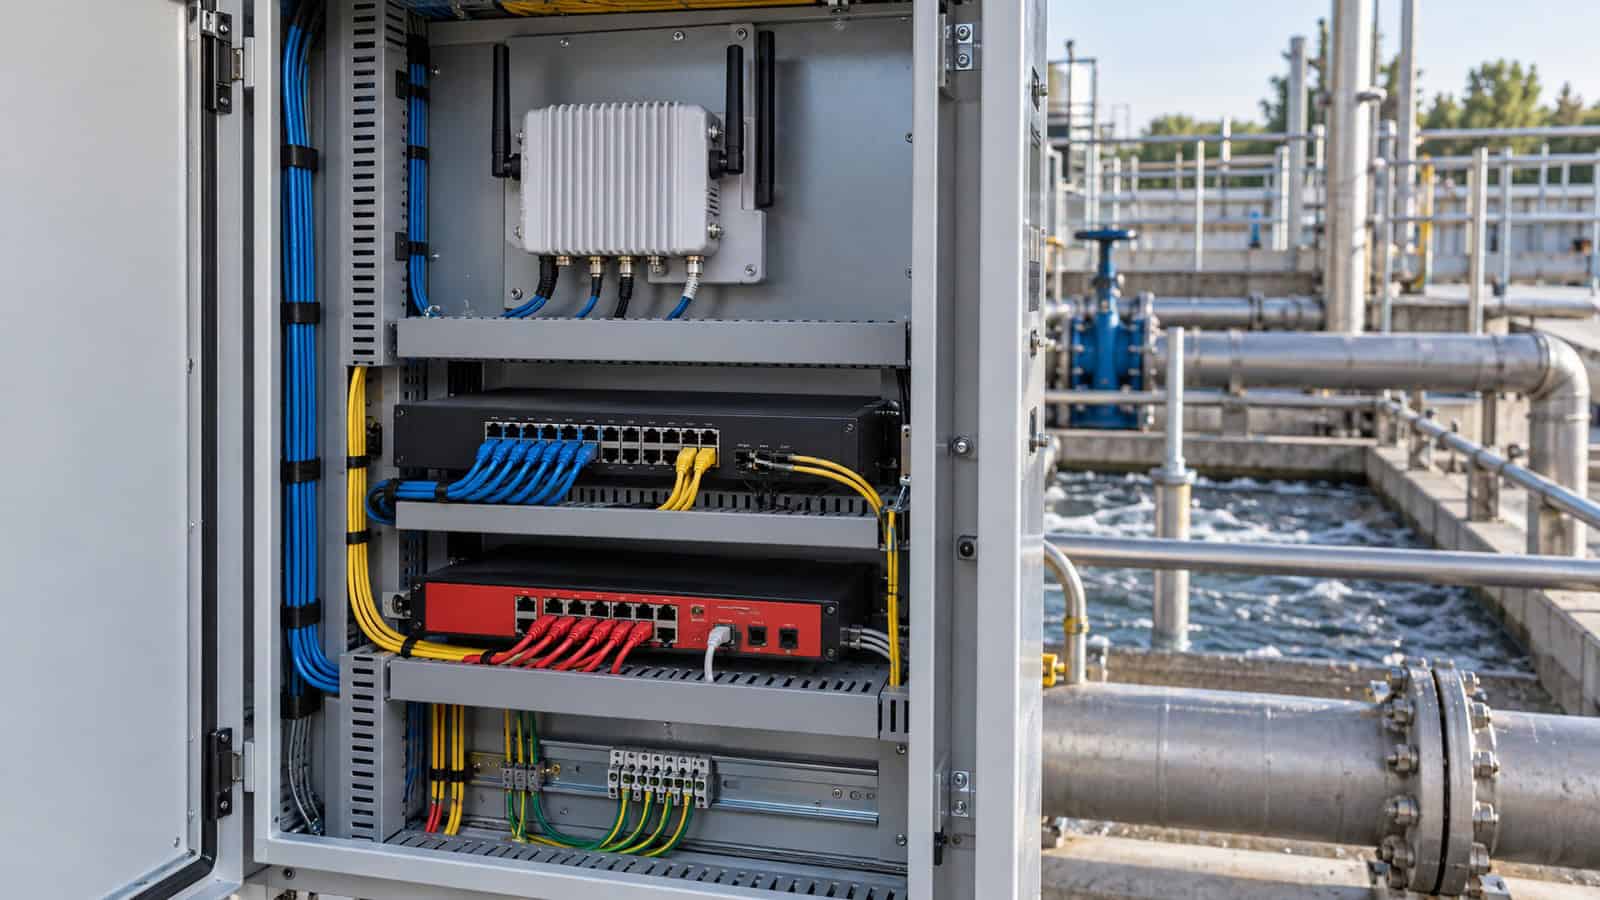
The Robustel LG3120e LoRaWAN Gateway is suited to projects that need LoRaWAN collection, local edge work and several upstream integration paths, but those roles should not be collapsed into one trusted LAN. A secure design separates gateway management, LNS traffic, application data and any local OT interfaces, then proves that required flows survive without broad “any-to-any” rules.
Draw Four Planes, Even if They Share One Cable
The radio plane carries LoRaWAN frames. The LNS plane handles gateway-server communication and device sessions. The application plane carries decoded or transformed data northbound. The management plane configures and monitors the gateway itself. They may share Ethernet or cellular transport, but they have different identities and owners.
Start with a flow register rather than a VLAN list:
| Source | Destination | Service/purpose | Owner | Behaviour if blocked |
|---|---|---|---|---|
| Gateway forwarder | Selected LNS | LoRaWAN transport | LoRaWAN team | Frames remain local or are lost per design |
| Edge application | BMS/cloud endpoint | Decoded data | Application owner | Local collection may continue |
| Admin workstation | Gateway management | Approved maintenance | OT/IT owner | No remote change |
| Gateway | NTP/DNS | Time and name resolution | Infrastructure | Logs or connections degrade |
VLANs Contain Broadcast Domains; Firewalls Enforce Intent
A VLAN tag does not create a security policy on its own. Terminate each zone at a device that can enforce allow-lists, log denied connections and handle the return path. Keep the management interface out of general application segments and avoid exposing it directly to the public internet.
Test name resolution and time sync explicitly. Teams often allow the obvious LNS address and forget NTP, DNS or certificate-validation dependencies. The result can be an apparently healthy IP link with unusable timestamps or TLS sessions.
Robustel’s Voytech BMS case study uses the R1520LG, but its layered building architecture remains useful here: LoRaWAN devices, the gateway, server and BACnet-facing system have distinct roles. For an LG3120e design, use that separation to build the zone map and then populate it with the interfaces and services selected for the LG3120e and E2C Field deployment.
LNS Placement Changes the Firewall Model
An external LNS requires a controlled outbound path and a clear policy for reconnect and buffering. An LNS at the site reduces dependence on the WAN for local LoRaWAN functions but adds local server maintenance and backup. State which option the project uses; “supports LoRaWAN” is not enough to derive firewall rules.
Record gateway identity, server certificate ownership, permitted destinations and whether cellular and Ethernet paths use the same policy. During commissioning, block the LNS path while leaving management available, then reverse the test. The operator should be able to distinguish the two states.
The Robustel video “What Is a LoRaWAN Gateway?” is useful preparation for colleagues who need the gateway-versus-LNS distinction before the firewall workshop. The implementation discussion should then return to the selected LG3120e interfaces, E2C Field configuration and the project’s own trust zones.
Bind Applications to Exact Interfaces and Trust Zones
Local serial, Ethernet or I/O data may be combined with LoRaWAN data, but the edge application must define the transformation and northbound contract. Keep credentials outside application images where possible, restrict container privileges and document persistent data. If a protocol is not listed for the selected application, do not imply native support merely because Linux or Docker is available.
The Robustel’s smart-building LoRaWAN application example illustrates the separation between field sensing, gateway/LNS and BMS integration. Use it as an architecture reference; project protocol support still follows the deployed application and configuration.
How the Robustel LG3120e LoRaWAN Gateway and E2C Field Support a Clear Data Boundary
The Robustel LG3120e LoRaWAN gateway combines LoRaWAN, LTE/eSIM connectivity, Ethernet, Wi-Fi and industrial interfaces with RobustOS Pro for supported local applications. On this exact compatible model, Robustel E2C Field can bring LoRaWAN configuration, data collection, alarms, workflows and northbound integration into one managed field application.
That pairing can reduce the number of hand-built components between sensors and the consuming system: the gateway provides the verified radio, interfaces, compute and backhaul, while E2C Field makes collection and operations more visible. A clearer deployment boundary also makes segmentation easier to operate, provided management, LNS and northbound destinations keep their own governed paths.
Use Robutsel RCMS platform for supported device-fleet operations and E2C Field for its documented application role.
Commission With Selective Failure
Block one dependency at a time: DNS, NTP, LNS, northbound application and remote management. Observe what remains local, which alarm appears and what is replayed when the rule is restored. Save firewall logs and application timestamps with the test record.
The final diagram should show addresses, VLANs, allowed services, certificate owner and recovery owner. If a replacement engineer can restore the intended flows without opening a broad temporary rule, the segmentation is operational rather than decorative.
FAQs
Q1. What is network segmentation?
It divides systems into controlled zones and limits communication to required paths. The objective is to reduce fault and attack propagation while keeping approved operations usable.
Q2. Is a VLAN the same as a firewall?
No. A VLAN separates Layer 2 broadcast domains; a firewall applies rules between networks or zones. Secure segmentation normally needs both addressing structure and enforced policy.
Q3. What ports does a LoRaWAN gateway need open?
That depends on the packet-forwarder or Basics Station method, LNS destination, DNS, NTP and management design. Build an allow-list from the selected architecture instead of copying a universal port list.
Q4. Should a LoRaWAN gateway be on the corporate LAN?
It should be placed in a zone that matches its risk and data flows, usually with explicit routes to the LNS, management and application services. Direct membership of a broad user LAN is rarely necessary.
Q5. What does the Robustel LG3120e LoRaWAN Gateway with E2C Field add?
The supported pairing combines gateway connectivity and local compute with LoRaWAN configuration, data collection, alarms, workflows and northbound integration. It still needs a designed network boundary for management, LNS and application traffic.
Conclusion
The Robustel LG3120e LoRaWAN Gateway provides the interfaces and local application platform for a well-segmented field design, while E2C Field can make the compatible model’s LoRaWAN data workflow easier to operate and observe. Security improves when every flow has a destination and owner, not when more functions are hidden behind one trusted address.
Prove the design by breaking individual dependencies and reading the resulting evidence. A firewall matrix that survives that exercise is ready to become an as-built control.
Explore More Articles About Robustel LoRaWAN Gateways
About the Author
Robustel Editorial Team
The Robustel Editorial Team publishes practical articles on industrial connectivity, edge computing, LoRaWAN and device management, focusing on deployment considerations, technical limitations and long-term operation.